Technical Overview
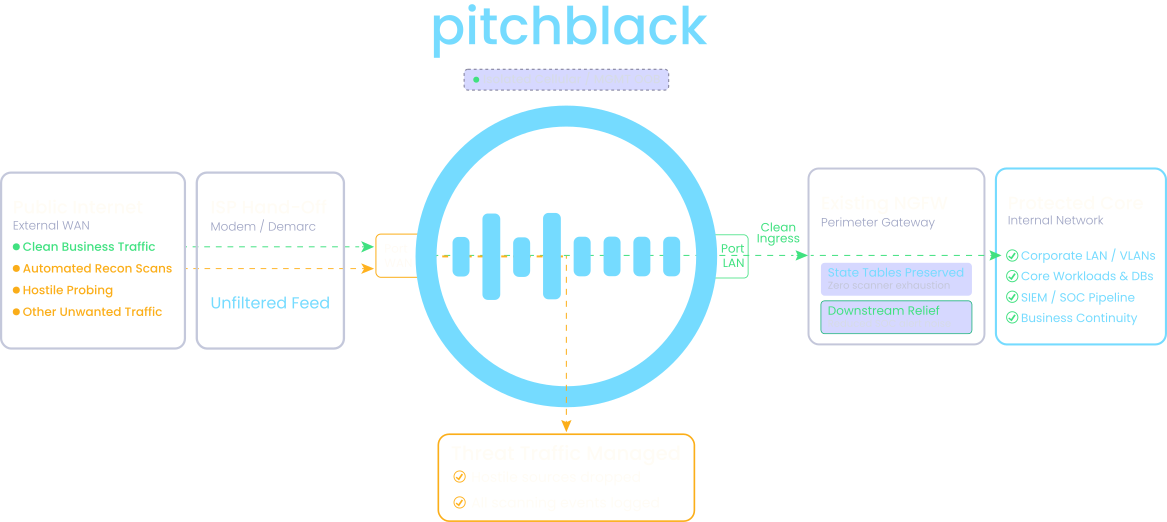
PitchBlack is a cybersecurity appliance that sits at the network perimeter. It operates as a transparent layer 2 bridge, and monitors inbound traffic, automatically blocking hostile sources at the edge.
PitchBlack complements your existing firewall, VPN and network security stack.
Placement and Topology
PitchBlack operates as a true layer 2 bridge between the ISP handoff and your downstream firewall or gateway.
Strengthen Your Stack
PitchBlack adds a pre-firewall hygiene layer. It sheds hostile sources before they can exhaust firewall state tables. This reduces downstream noise and covers the perimeter path that host-level tools cannot see.
Features
- Autonomous edge defense barrier
- Proxy server
- API integration
- Automated event logging
Telemetry
- Outbound log export and telemetry formatting for standard SOC tooling, including Syslog and SIEM ingestion.
- Complete separation between the out-of-band management plane and the inline data path.
- Intelligence without decryption; PitchBlack never decrypts or inspects packet content.
- Optional destination blocking is off by default and is never applied to shared CDN addresses.
- Optional notifications when blocking events occur so edge activity shows up in your existing tools.
What PitchBlack Adds
- NGFW: Helps prevent state-table exhaustion
- SIEM: Fewer events enter the detection pipeline
- SOAR: Blocking events surfaced for automation playbooks
- NDR: Edge-path view of hostile sources
- Telemetry exported to SOC tooling
What It Does Not Cover
- NGFW: Policy control/deep traffic policy
- SIEM: Log analytics and correlation
- SOAR: Orchestration and response workflows
- EDR: Endpoint agents and host context
- NDR: Internal and east-west detection
- Traffic that doesn't cross the device
Field Testing and Methodology
First 48-Hours Single-Site Observation
Security events processed automatically
threat sources stopped at the boundary
countries among blocked threat sources
0
false positives
0
human interventions
0
disruption
58-Day Dual-Site observation
257,050
events observed
2,790
Blocked sources
34,693
Unique sources observed
115
Countries
~30 mins
Average time between blocks
0
confirmed false positives
Methodology Summary
- Figures come from production telemetry during the stated windows.
- Events are counted per observed connection, and sources correspond to unique addresses observed in the window.
- Blocked sources represents unique hostile sources automatically blocked during the window.
Frequently Asked Questions
What Is the Implementation Process?
Implementation is swift, simple, and requires no network configuration or firewall changes. Our technicians install the device on location with a standard port configuration. Network downtime is typically limited to under an hour.
Do You Offer A Trial Period?
Yes, trials may be arranged on a case-by-case basis.
Is There An Allowlist?
Yes, specific sources may be whitelisted.
Are guest Wi-Fi and VPN users covered?
Coverage is path-based. When guest or VPN traffic crosses the device, it is protected like any other traffic on that path. Traffic that bypasses the device is outside its scope.
Are the contents of traffic inspected or observed?
No. The contents of traffic that crosses the device are never decrypted, inspected, or observed.
How is this different from my Firewall?
Firewalls block traffic based on a pre-defined set of rules. PitchBlack’s unique approach identifies attack traffic without inspecting packet content or relying on ephemeral blocklists.
Augment Your Network Security
PitchBlack is a cutting edge addition to the cybersecurity paradigm designed for the AI threat landscape. Request a briefing to learn how you can integrate PitchBlack into your stack.